


Cut the cord on VPNs
Modernize the legacy infrastructure holding your agency back. Give every user, in any office or agency, fast zero trust access to the apps and systems they need. No legacy hardware, no bottlenecks.




Modernize the legacy infrastructure holding your agency back. Give every user, in any office or agency, fast zero trust access to the apps and systems they need. No legacy hardware, no bottlenecks.
Track citizen records, case files, and constituent data everywhere it goes across SaaS, cloud, web and AI. Stop it the moment it heads somewhere it shouldn’t.
Get full visibility into shadow AI, managed tools, and autonomous agents. Coach users through risky moments in real-time, block sensitive data before it leaves, and keep your agency moving fast with AI.
Netskope One replaces a patchwork of VPNs, branch firewalls, and point tools with one converged platform, delivered over a private global cloud built for speed.
Converge networking and security, including zero trust network access, web gateway, CASB, and SD-WAN, into a single, cloud delivered platform. Replace slow, high risk VPNs with fast, least-privilege access, without adding another point product to manage.

Track and protect citizen records, case files, and constituent data across SaaS, web, cloud, and AI with one consistent policy enforced everywhere it travels.

From shadow AI and public chatbots to private models and autonomous agents, Netskope covers the full AI lifecycle, discovering usage, controlling access, protecting data, coaching risk behavior, and testing for vulnerabilities before anything reaches production.

Every connection runs through Netskope’s private global cloud, so agencies get fast, reliable performance without trading speed for protection.
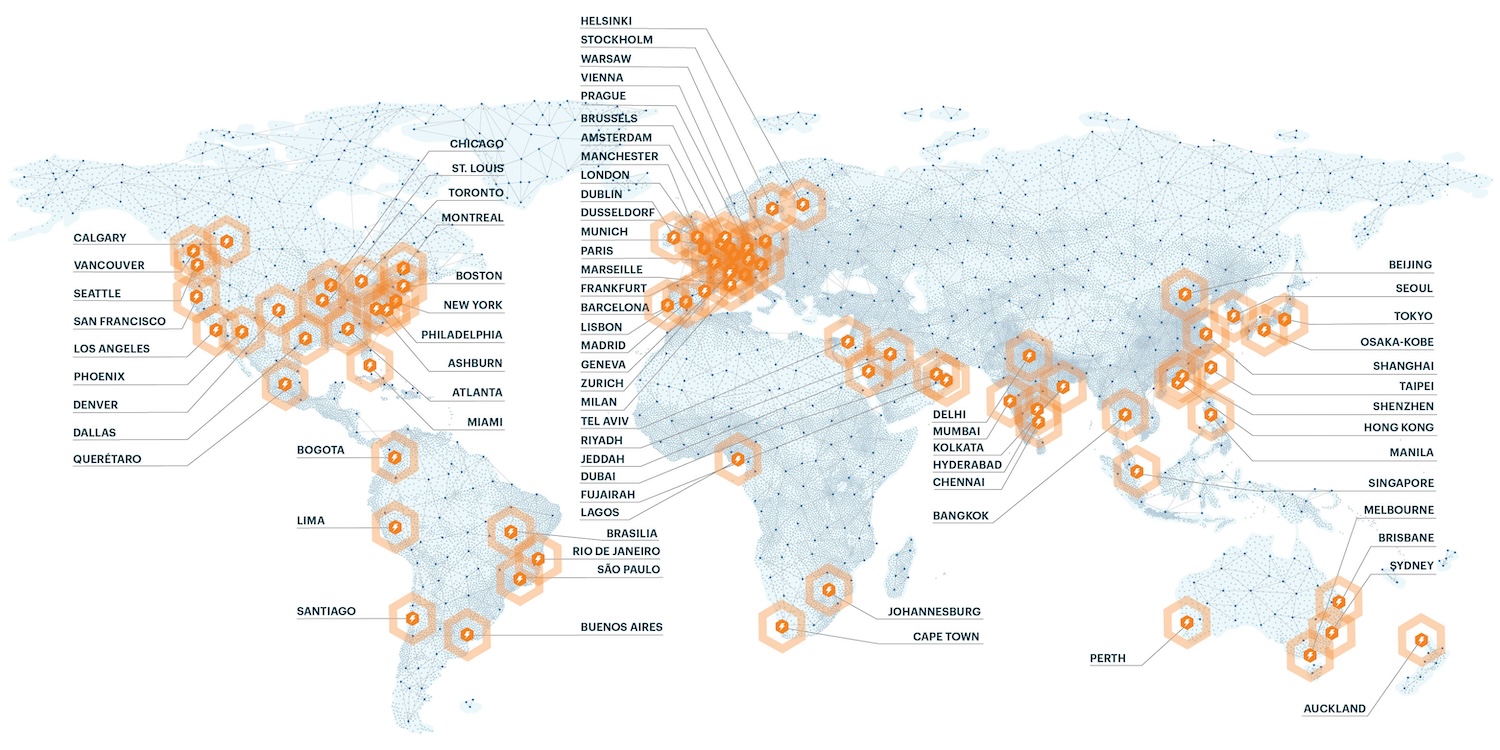
From remote access to AI, one platform to solve your agency’s toughest challenges.
)
VPN exploitation is now the single most common way attackers get into government networks. Netskope replaces slow, exploitable VPNs with fast, least-privilege zero trust access instead. Users get the access they need without giving attackers a way in too.
From an accidental email to a risky AI prompt, sensitive data can leave your agency in seconds. Netskope catches it automatically, whether it’s a case file, tax record, or benefits file, before it becomes a breach report. Built-in accuracy cuts the false positives your team has to chase down.
Ransomware and encrypted threats slip through tools that only inspect traffic in pieces, one gap is all it takes. Netskope decrypts and scans all web, cloud, and private app traffic in a single pass, using AI/ML detection and real-time sandboxing to catch what signature-based tools miss, before it ever reaches city networks or case systems.
Netskope finds every AI app, model and agent in use across your agency. It then governs the full lifecycle: controlling access, blocking sensitive data from leaving, coaching risky prompts in the moment, and stopping attacks such as prompt injection before they succeed.
Every county, city, and school district deserves the same level of protection as the state itself, not a patchwork of one off deployments. Netskope enables a state to extend one platform, and one set of controls mapped to NIST CSF and FedRAMP High, to every jurisdiction that needs it.
Agencies run on M365, AWS, Azure, and GCP, but most IT teams can’t see every app, misconfiguration, or unmanaged SaaS tool running underneath them. Netskope gives full visibility and control across every cloud and SaaS app in use, managed or not, enforcing one consistent policy instead of a patchwork of settings. Shadow IT stops being a blind spot, and becomes just another thing your team has covered.
VPN exploitation is now the single most common way attackers get into government networks. Netskope replaces slow, exploitable VPNs with fast, least-privilege zero trust access instead. Users get the access they need without giving attackers a way in too.
From an accidental email to a risky AI prompt, sensitive data can leave your agency in seconds. Netskope catches it automatically, whether it’s a case file, tax record, or benefits file, before it becomes a breach report. Built-in accuracy cuts the false positives your team has to chase down.
Ransomware and encrypted threats slip through tools that only inspect traffic in pieces, one gap is all it takes. Netskope decrypts and scans all web, cloud, and private app traffic in a single pass, using AI/ML detection and real-time sandboxing to catch what signature-based tools miss, before it ever reaches city networks or case systems.
Netskope finds every AI app, model and agent in use across your agency. It then governs the full lifecycle: controlling access, blocking sensitive data from leaving, coaching risky prompts in the moment, and stopping attacks such as prompt injection before they succeed.
Every county, city, and school district deserves the same level of protection as the state itself, not a patchwork of one off deployments. Netskope enables a state to extend one platform, and one set of controls mapped to NIST CSF and FedRAMP High, to every jurisdiction that needs it.
Agencies run on M365, AWS, Azure, and GCP, but most IT teams can’t see every app, misconfiguration, or unmanaged SaaS tool running underneath them. Netskope gives full visibility and control across every cloud and SaaS app in use, managed or not, enforcing one consistent policy instead of a patchwork of settings. Shadow IT stops being a blind spot, and becomes just another thing your team has covered.


Netskope upholds the highest standards of security, performance, and transparency to protect the federal government.
FedRAMP
FedRAMP is a government-wide program that provides a standardized approach to security assessment, authorization, and continuous monitoring for cloud products and services. The program enables government agencies to adapt from old, insecure legacy IT to mission-enabling, secure, and cost-effective cloud-based IT.
Learn more about Netskope’s Authorization.
AICPA SOC 2
Netskope System & Organization Control (SOC) Reports are independent third-party examination reports that demonstrate how Netskope achieves key compliance controls and objectives. The purpose of these reports is to help you and your auditors understand the Netskope controls established to support operations and compliance.
To request a copy of our SOC 2 report , please contact your account representative.
California Consumer Privacy Act
Netskope supports the customer’s compliance for Processing covered by the California Consumer Privacy Act of 2018 (the “CCPA”). To confirm applicable aspects of the CCPA in connection with Customer’s use of the Services, Netskope has provided this Compliance Statement. This notice supplements the Netskope Privacy Policy.
As part of its Health Insurance Portability and Accountability Act (HIPAA) compliance program, Netskope has been assessed against the controls in place to satisfy the requirements of the HIPAA Security Rule, as well as the requirements of the HIPAA Breach Notification Rule as formalized by the Health Information Technology for Economic and Clinical Health (HITECH) Act of 2009 and the Omnibus Rule of 2013.
To request a copy of our HIPAA Assessment Report, please contact your account representative.
ISO 27001
The International Organization for Standardization 27001 Standard (ISO 27001) is an information security standard that ensures office sites, development centers, support centers and data centers are securely managed. These certifications run for 3 years (renewal audits) and have annual touch point audits (surveillance audits).
To request a our ISO 27001 Certificate , please contact your account representative.
ISO 27017
ISO/IEC 27017 is a security standard developed for cloud service providers and users to make a safer cloud-based environment and reduce the risk of security problems.
To request the ISO 27017 certification, please contact your account representative.
ISO 27018 Certified
The International Organization for Standardization 27018 Standard (ISO 27018) covers privacy protections for the processing of personal information by cloud service providers.
To request a our ISO 27018 Certificate , please contact your account representative.


Netskope provides an open architecture with over 100 partners, direct integrations, and channel partners.
 |  |  |  |
 |  |  |  |
 |  |  |  |


Netskope protects municipal infrastructure by decrypting and inspecting all web, cloud, AI and private application traffic in a single pass, using AI-powered behavioral detection and real-time sandboxing to catch ransomware and zero-day threats that signature-based tools miss. Because exploited VPNs are one of the most common ways ransomware reaches local government networks, Netskope also replaces broad-access VPNs with zero trust network access, so a compromised credential can’t move laterally into case management, billing, or public safety systems.
Yes. Municipal, county, and state workers increasingly use generative AI to speed up administrative tasks and public communications, but pasting citizen data into a public AI tool creates a real compliance risk. Netskope discovers every AI app and model in use, then enforces real-time AI guardrails that automatically block sensitive data, such as tax records, case files, or citizen PII, from being submitted to public AI models. It also coaches users in the moment when a prompt looks risky, so agencies can build up better security practices within their workforce and adopt AI without creating new regulatory exposure.
Netskope holds FedRAMP High Authorization, the highest standard for government cloud security, and supports compliance with HIPAA, the California Consumer Privacy Act (CCPA), SOC 2/3 and ISO 27001, 27017, and 27018 frameworks. For state and local government teams specifically, Netskope maps its security controls directly to the NIST Cybersecurity Framework (CSF) v2.0, giving your IT team audit-ready visibility, continuous data isolation, and traceable reporting to prove compliance to state auditors.
Netskope lowers total cost of ownership by replacing a fragmented patchwork of point products, separate firewalls, web filters, and VPN appliances with a single converged SASE architecture managed from one cloud console. This eliminates redundant multi-vendor licensing, cutting expensive MPLS routing dependencies, and automating compliance reporting all reduce administrative overhead and deliver meaningful budget savings.
Legacy VPNs grant broad network-level access and become a top ransomware entry point once a single credential is compromised. Netskope replaces them with zero trust network access (ZTNA), granting each user access to the one application they need, not the whole network, without deploying or maintaining any hardware.


